







Realm: Modern Access Bastion & Sovereign PAM
Browser-based access bastion, no client software, no VPN
Heimlane Realm is a modern bastion host (PAM): browser-based RDP, SSH and VNC access, full session recording, and credential injection from Vault: administrators never see the password. No jump server, no firewall changes.
See Heimlane Realm in Action
Realm in action: a business, its team and its providers
Why This Bastion Host Is Different
Traditional access solutions, notably PAMs (also called access bastions or administration bastions), require expensive infrastructure, complex configuration, and dedicated teams.
Realm is a sovereign bastion, designed for the real needs of SMBs and mid-market companies, built around zero trust and least privilege principles.
No platform fee, no appliance to buy, no minimum commitment for MSPs: Realm is priced per user and operational in minutes.
What is a bastion host? Definition, mechanics, and use cases →
Replacing a VPN or a legacy bastion? How to switch without a big-bang cutover →
Every enterprise-PAM capability, without the complexity or the cost:
- Session recording
- Full traceability and audit
- Secure credential storage
- Role-based access control

- 100% browser access, no client to install
- Credentials handled by Heimlane Vault
- Operational in minutes
- No heavy infrastructure or dedicated team
Who it's for
Perfect for MSPs/MSSPs managing multiple customer environments, or businesses needing secure remote access without the complexity of enterprise solutions.
Simple Interface, Professional Power
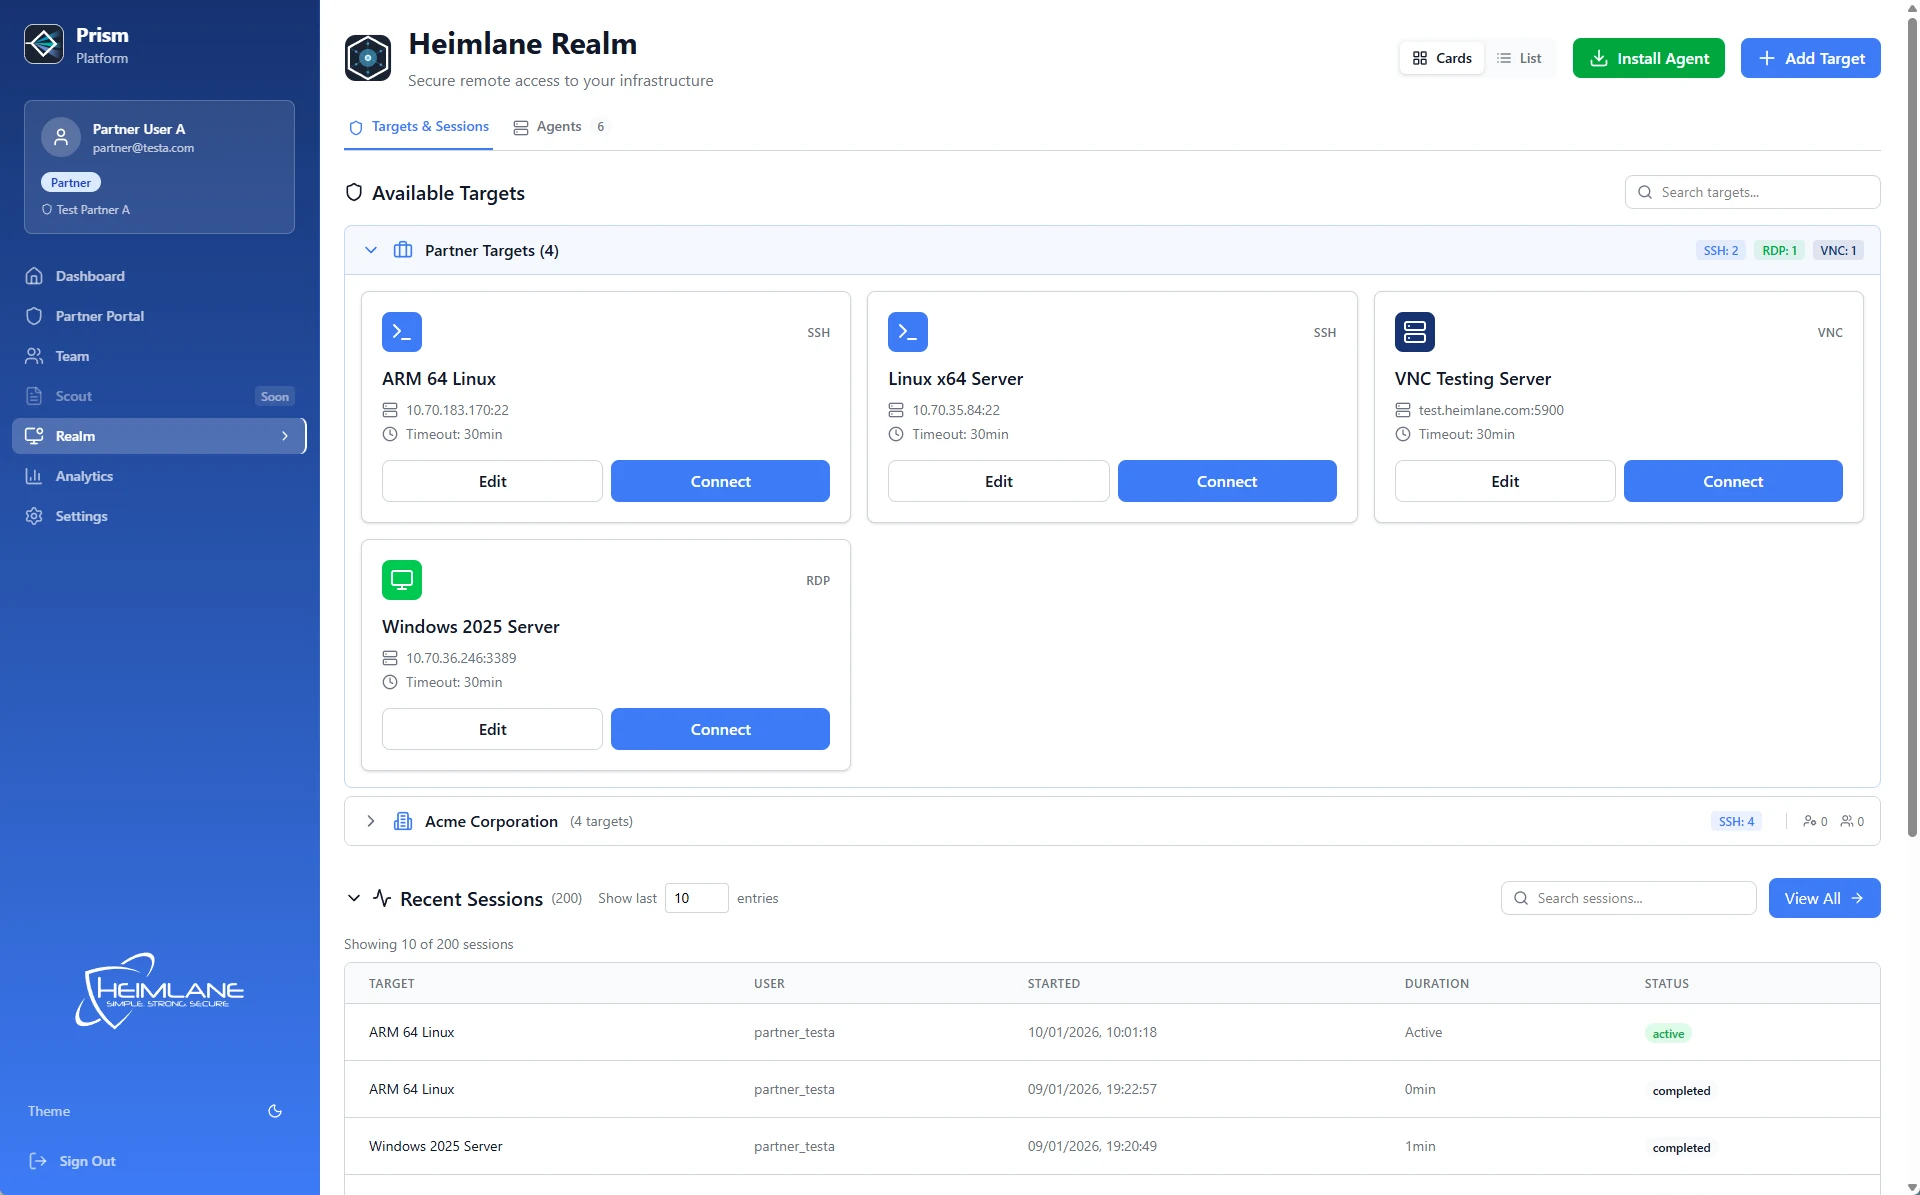
Heimlane Realm centralizes all your remote access in a clear, intuitive interface. Create your targets in just a few clicks and connect instantly, straight from your browser.
The complete session history lets you track who accessed what, when, and for how long. Perfect for compliance, auditing, and incident response.
Vendor access, just in time
Give an outside provider exactly the access the job needs, for exactly as long as it takes. Then nothing.
Just-in-time (JIT) vendor access

Invite an external vendor to a single machine, right now or on a schedule, for example weekdays from 8:00 to 13:00. Each access is approved, tied to the vendor's email address, recorded, and closes on its own when the window ends.
No standing account, no shared password: the credential is injected, never handed over.
Bring an expert into a live session

Stuck on a problem? Invite a specialist into the session you have open, watch-only or with control, and remove them the moment you are done. The whole exchange stays on the session record.
Live session watching

Authorized administrators and auditors can follow a privileged session as it happens, read-only, and end it immediately if something looks wrong.
Every termination is written to the audit trail, with who ended the session and why.

Take Back Control Now
Within minutes, your access is managed, audited, and compliant.
The Bastion in Detail: SSH, RDP, and VNC
Zero-knowledge access

Credentials never leave Heimlane Vault unencrypted.
Heimlane has no access to the credentials of your machines.
A bastion you reach from the browser

SSH, RDP, and VNC sessions directly in your browser, from any device. No jump server, client software, or VPN configuration: a modern HTML5 browser is all you need.
Vault integration

Automatic credential injection from Heimlane Vault.
Your administrators use the password without ever seeing it. Every use is logged for audit.
Session recording

Automatic recording of the complete session for audit, compliance, and your security reviews
Role-based permissions

Fine-grained control over who accesses what, based on actual and segmented needs, not ''because the VPN is configured that way''
Audited administration bastion

Grant controlled access to your teams and third parties following the principle of least privilege.
Use automatic recording of all actions for audit and investigation purposes
Multi-tenant ready

MSPs can manage multiple customer environments seamlessly
Easy setup, multi-protocol support

Setup in just a few clicks
Support for SSH, RDP, VNC protocols, all from one interface

Get the Realm Datasheet
Download our detailed product datasheet, covering features and technical specifications.
Download DatasheetFrequently asked questions about Realm
Can Realm replace our current bastion?
Do we need a jump server or a firewall opening?
Which protocols does the Realm bastion support?
How are credentials protected during a session?
Does Realm suit a multi-customer bastion setup?
Can we give an outside vendor temporary access without sharing a password?
Can we watch a privileged session while it is happening?
How is Realm priced?
Ready to Get Started?
Request a trial or a demo to get started.
Priced per user. No platform fee, no minimum commitment for MSPs.